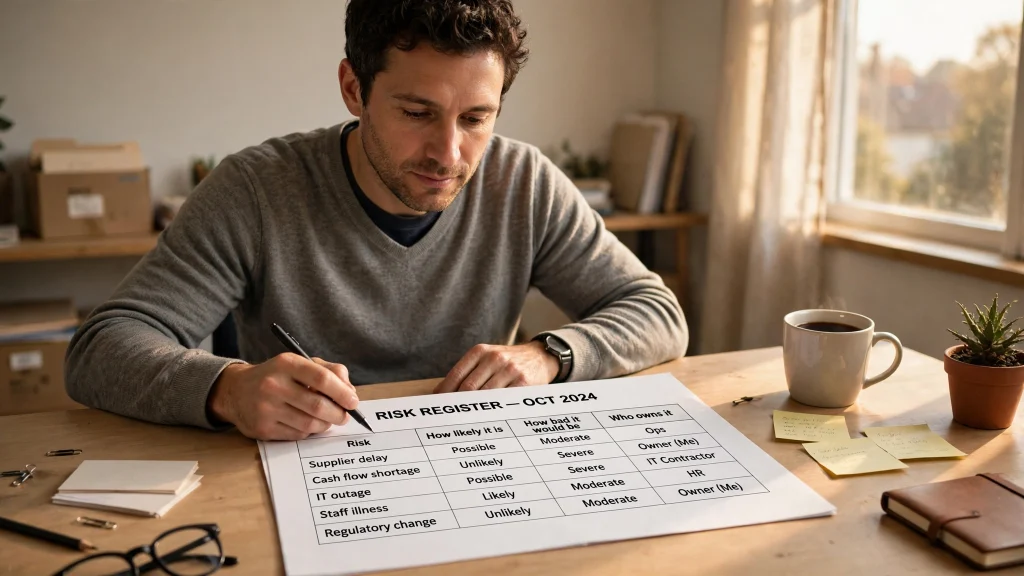
Risk Management, in Plain English
Risk management is finding what could hurt your business, judging how likely and how bad it is, and deciding — in writing — what to do about it.
Risk identification and assessment methodologies for business continuity, including threat modeling and vulnerability analysis.
Risk management is finding what could hurt your business, judging how likely and how bad it is, and deciding — in writing — what to do about it.
A restoration company can make its revenue for the whole year in one quarter, depending on the weather. That cuts
Vendor cyber incidents are continuity events. The three transmission paths from a supplier incident to your outage, the contract levers that decide the day, and the replacement lead time every BIA should carry.
A risk register is a workload, not a workshop souvenir. The fields that earn their place, inherent versus residual honesty, and the review cadence that keeps the register alive.
The risk matrix is the most-used and most-abused picture in the discipline. Build it on anchored scales, plot inherent and residual honestly, and know the three pathologies that make it lie.
When Microsoft Copilot goes down or an AI-powered workflow tool fails, how long before operations halt? AI dependency has become the single-point-of-failure risk most BC plans haven’t addressed.
ISO 22301’s 2024 amendment explicitly requires climate scenario integration. In 2026, BC programs without climate-adapted risk assessments are operationally and legally exposed.
A method guide for building a business impact analysis and recovery priorities. This page is not a software generator and will not produce a BIA for you.

Published: April 2026 | Category: Risk Assessment What is Climate-Adapted Business Continuity? Climate-adapted business continuity integrates physical climate risks (hurricanes,
Home / Categories / Disaster Recovery Disaster Recovery Featured video analysis and expert resources 🔥 The Ultimate Guide to Disaster
A risk assessment is a decision document disguised as an analysis. Its job is not to list everything that could
Three frameworks dominate enterprise risk assessment, and they are not interchangeable. ISO 31000 is a set of principles and guidelines